Zero Trust in Manufacturing: What CMMC Assessors Should Understand About OT
Explore how Zero Trust principles intersect with manufacturing OT, CMMC assessment scope, and operational realities assessors should understand.
Explore how Zero Trust principles intersect with manufacturing OT, CMMC assessment scope, and operational realities assessors should understand.
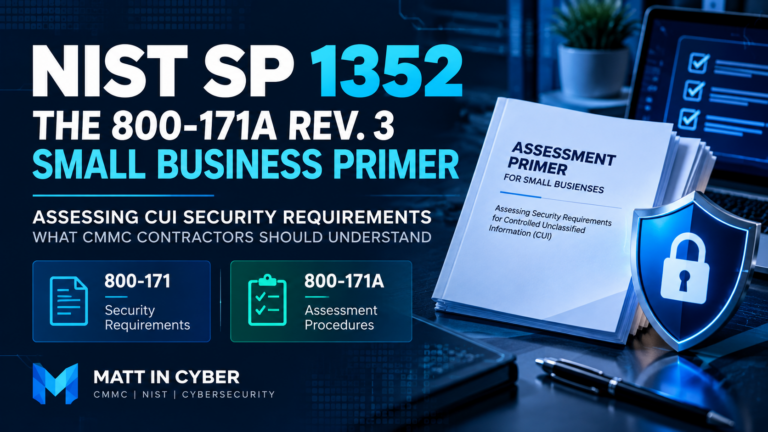
NIST has published SP 1352, a new small business primer for SP 800-171A Rev. 3. Here is what CMMC contractors should understand about the new assessment resource and the important distinction between NIST Rev. 3 guidance and current CMMC requirements.
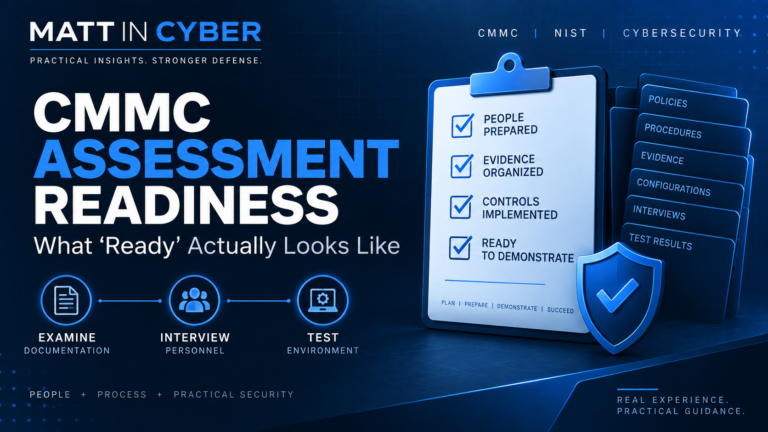
A CMMC assessment is not simply a review of policies, screenshots, and compliance documents. Organizations preparing for an assessment need to be able to demonstrate that their cybersecurity requirements are implemented in the environment, understood by the people responsible for them, and supported by evidence that reflects how the organization actually operates. That distinction is…
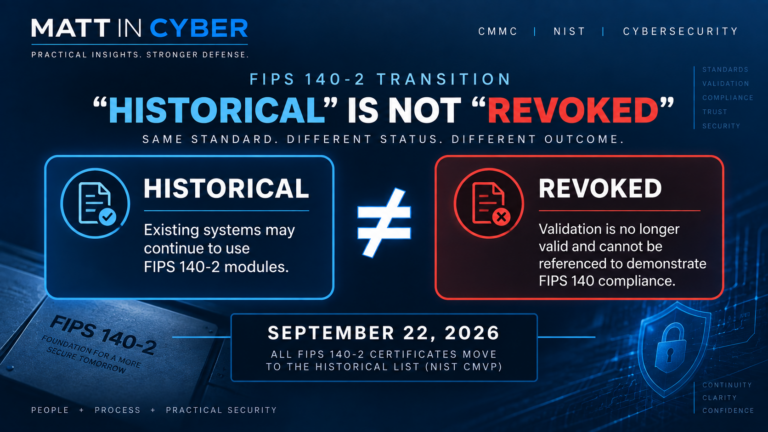
FIPS 140-2 certificates have moved to the CMVP Historical list, but Historical does not mean Revoked. Here’s what those statuses actually mean and why the distinction matters.
FIPS 140-2 validated modules move to the CMVP Historical list in September 2026. Here’s what the transition means for CMMC environments and how organizations should prepare for FIPS 140-3.